

NEW DELHI: The State Bank of India (SBI) has disclosed a suspected cyber incident involving the exposure of 3,897 customer records containing personally identifiable information, potentially available on the dark web.
In a filing with stock exchanges, the country’s largest public sector bank said it received an alert on October 16 from its threat intelligence service provider, the Defence Cyber Agency and the Indian Computer Emergency Response Team (CERT-In) regarding the suspected exposure.
According to SBI, a preliminary analysis of approximately 3.75 lakh records found on the dark web identified 3,897 customer records containing personal information. The potentially exposed details include registered mobile numbers, dates of birth, names, gender, email addresses and residential addresses.
The records also reportedly contained branch details, Customer Information File (CIF) identifiers, lead IDs and metadata associated with loan and lead records and related files.
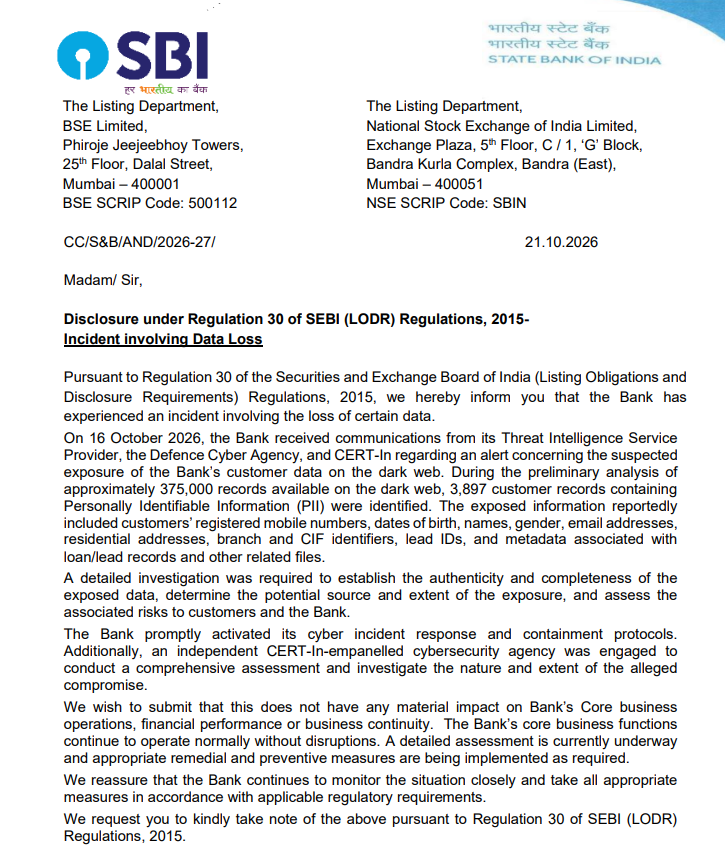
SBI clarified that the incident had not materially affected its core operations, financial performance or business continuity. The bank said its core business functions continued to operate normally and that cyber incident response and containment protocols had been activated promptly.
The bank added that a detailed investigation was required to establish the authenticity and completeness of the exposed data, identify its possible source, determine the extent of the breach and assess potential risks to customers and the institution.
SBI said it was closely monitoring the situation and would take appropriate measures in accordance with applicable regulatory requirements as the investigation continued.
Earlier, India Today Tech reported claims by an anonymous hacker group identified as Siriusim, which allegedly claimed on the dark web forum BreachForums to have obtained information relating to 3.75 lakh SBI customers. SBI has not publicly identified the group responsible for the suspected incident.
The disclosure comes amid growing regulatory attention to cybersecurity in the banking sector. In July, Bank of Baroda acknowledged a data leak involving approximately 1TB of customer data, according to media reports.
The SBI investigation is ongoing, and the full extent and authenticity of the suspected data exposure remain to be established.
